6 Best Cloud Platforms for Securing Code Options for 2026

- Top of the list is GitHub Advanced Security, which targets teams standardized on GitHub.
- Free plans exist at 3 of 6 tools (Snyk, Semgrep, Sonar).
- Checkmarx suits enterprises needing deep SAST and compliance.
- GitHub Advanced Security, Veracode and Checkmarx: pricing is by quote only, so plan time for a sales conversation.
- Before buying Semgrep, weigh this: rule writing needed for depth, managed rules fewer than Snyk, smaller company, enterprise features tiered.
Direct answer
This list puts GitHub Advanced Security first for teams standardized on GitHub. Look at Veracode for policy-driven AppSec with compliance proof, and at Snyk for developers who want security in their workflow. Details, prices and limits for the rest of the 6 tools are below.
Quick comparison
| Product | Ideal for | Price from | Free version | |
|---|---|---|---|---|
 GitHub Advanced Security | Teams standardized on GitHub | See website | No | Visit |
 Veracode | Policy-driven AppSec with compliance proof | See website | No | Visit |
 Snyk | Developers who want security in their workflow | Free; premium plans see website | Yes | Visit |
 Semgrep | Quick custom rules developers actually write | Free; premium plans see website | Yes | Visit |
 Sonar | Catching bugs and vulnerabilities together | Free; premium plans see website | Yes | Visit |
 Checkmarx | Enterprises needing deep SAST and compliance | See website | No | Visit |
Tool-by-tool breakdown
Short on time? The summary and table above give the quick view of 6 tools for cloud platforms for securing code, and the profiles that follow give the detail behind each entry.
GitHub Advanced Security
Ideal for: Teams standardized on GitHub
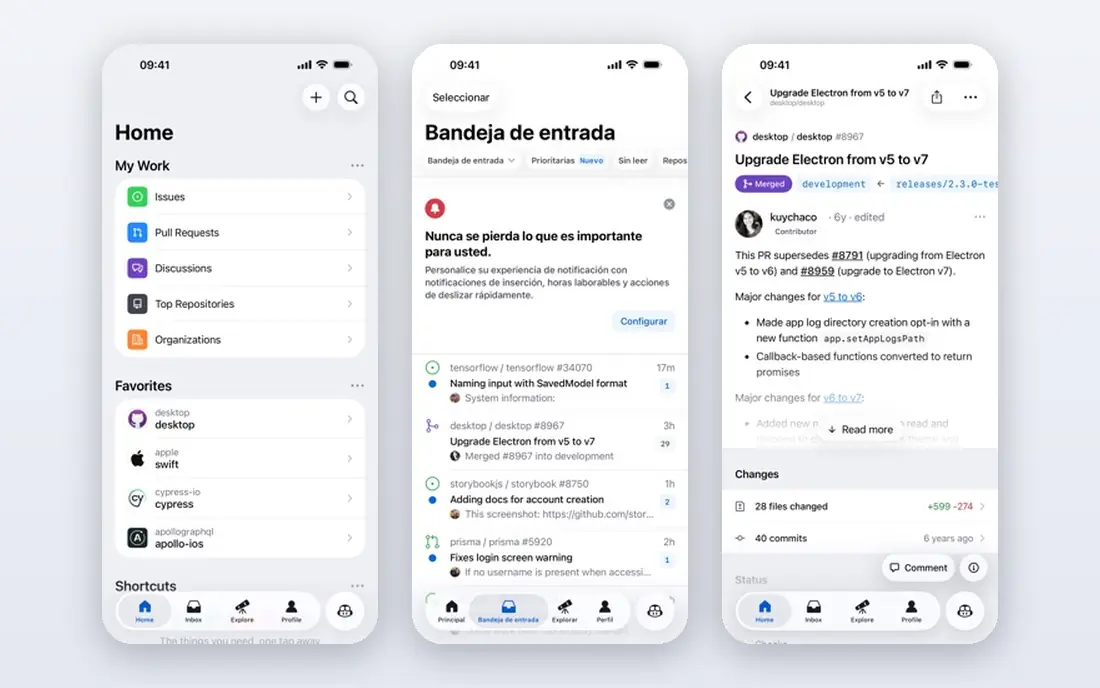
GitHub Advanced Security is built with teams standardized on GitHub in mind. Pricing is per active committer, which layers on up.
On top of that, depth trails Snyk and Checkmarx in spots, but the zero-friction adoption wins for GitHub shops. In daily use, enable autofix for the high-confidence rules and watch fix rates climb. Check the vendor site for GitHub Advanced Security pricing; none is listed in this comparison. GitHub Advanced Security does not include a free plan.
Downsides: less deep than specialists, best within GitHub, advanced features tiered.
- Native code scanning and secret scanning
- No new tool to learn
- Per-committer pricing
Veracode
Ideal for: Policy-driven AppSec with compliance proof
For policy-driven AppSec with compliance proof, Veracode is a natural candidate. Veracode provides static, dynamic, SCA and manual testing with policy enforcement and reporting that auditors accept. Veracode's mitigation proposals let developers document why a finding does not apply, with security approving.
What Veracode does well: policy and reporting strength.
Points against: Pricey, developer experience dated.
That workflow turns noise into decisions rather than ignored alerts. Regulated industries value the maturity. Also, developer experience lags newer tools and pricing is enterprise. Veracode does not show a starting price in this comparison, so check the vendor site for current pricing. Veracode has no free plan.
- Mature product
- Trusted in regulated industries
- Scan times can be slow, sales-led
Snyk
Ideal for: Developers who want security in their workflow
Snyk serves developers who want security in their workflow. The free level includes individuals and small teams well.
Points against: some scans need tuning, enterprise features tiered.
Reasons to shortlist it: excellent IDE and PR integration.
Snyk meets developers where they work: IDE plugins, pull request checks and automatic fix pull requests across open-source, code, containers and infrastructure as code. Alert volume needs triage discipline, and per-developer pricing brings up. On cost, Snyk starts like this: Free. Snyk offers a free plan.
- SAST
- Fix PRs automatic
- Pricing scales with developers
Semgrep
Ideal for: Quick custom rules developers actually write
Semgrep was built for quick custom rules developers actually write. Out-of-the-box rule depth trails managed products. Worth adding: Security-conscious engineering teams that write their own rules love it.
For everyday use, write the rule, measure the false positive rate, then deploy. Semgrep's rule playground lets security engineers test custom rules against real code before enforcing. Semgrep starts at: Free. Semgrep includes a free tier.
Where it falls short: managed rules fewer than Snyk, smaller company, enterprise features tiered.
- Blazing quick scans
- Ample free level
- Rule writing needed for depth
Sonar
Ideal for: Catching bugs and vulnerabilities together
Sonar was built for catching bugs and vulnerabilities together. Pure security depth is less than Snyk or Checkmarx.
Reasons to shortlist it: quick PR analysis; free for open source.
For everyday use, Sonar, via SonarQube Cloud, examines every pull request for bugs, code smells and vulnerabilities together. Price to start with Sonar: Free. A free plan is available with Sonar.
- Clean code methodology
- Code quality plus security
- Security depth less than pure AppSec, rules need tuning, enterprise features premium, UI utilitarian
Checkmarx
Ideal for: Enterprises needing deep SAST and compliance
Checkmarx is aimed squarely at enterprises needing deep SAST and compliance. Checkmarx provides one of the deepest static analysis engines with wide language coverage and compliance-ready reporting.
Highlights: wide language support.
Also, Checkmarx's custom queries let security teams encode organization-specific rules: dangerous internal APIs, banned patterns, compliance requirements. For depth and compliance over developer delight, it leads. Pricing for Checkmarx is not stated here, so ask the vendor for current figures. No free plan comes with Checkmarx.
- Mature enterprise features
- Deep SAST engine
- Pricey, complicated, developer experience improving, implementation effort
Worth knowing about cloud platforms for securing code
Securing code means finding vulnerabilities before they ship: in your own code with static analysis (SAST), in open-source dependencies with software composition analysis (SCA), in containers, and in secrets accidentally committed. On top of that, the shift is developer-first: security that blocks merges with clear fix guidance beats PDF reports nobody reads.
How the list was put together
Pricing pages, product documentation and feature lists were the main sources, and every entry carries at least one honest drawback. Figures are shown as the vendors publish them. Billing terms, seat minimums and add-ons can change the real cost. Position on the page reflects fit for a typical buyer first, with price clarity and free access breaking ties. Treat it as a guide, not a ruling.
What to confirm before you sign up
- Get a written quote from GitHub Advanced Security, Veracode and Checkmarx; the list shows no starting price for them.
- Look at free plan limits closely: Snyk, Semgrep and Sonar have one, and the caps decide whether it is usable for real work.
- Before choosing GitHub Advanced Security, weigh its main limit: per-committer pricing, less deep than specialists, best within GitHub, advanced features tiered.
- Look at the renewal terms for Sonar: auto-renewal, notice periods and price changes can matter more than the first-year price.
- Read the plan comparison for Veracode carefully; key features often start on a higher tier.
Frequently asked questions
Do these tools publish their prices?
Not all of them. GitHub Advanced Security, Veracode and Checkmarx publish no starting price, so expect a quote request for those. The rest, Snyk included, show a starting price, though seats and billing terms still change the final cost.
Is GitHub Advanced Security the right pick for everyone comparing cloud platforms for securing code?
No single tool suits every team. GitHub Advanced Security comes first because it fits teams standardized on GitHub, while Veracode suits policy-driven AppSec with compliance proof and Snyk suits developers who want security in their workflow. Match the tool to your own size, budget and workflow before deciding.
Which options for cloud platforms for securing code have a free plan?
On this list, Snyk, Semgrep and Sonar include a free plan. Caps on seats, usage or features are common, so test the free plan against your real workload.
How are the tools for cloud platforms for securing code ordered?
GitHub Advanced Security sits first and Checkmarx last because the order follows typical fit for cloud platforms for securing code, then price clarity and free access. It is a judgement call, so read each profile for fit and limits.