Best GRC Compliance Platforms in 2026: 8 Platforms Compared

- 1
 VantaIntegration breadthVisit
- 2
 DrataMulti-framework monitoringVisit
- 3
 SecureframeGuided SMB onboardingVisit
- 4
 AuditBoardEnterprise GRC and auditVisit
- 5
 ServiceNow GRCServiceNow ecosystemsVisit
- Vanta leads on integration breadth for compliance automation, with Essentials pricing from $14,000 per year in marketplace listings.
- Drata wins on continuous-monitoring experience and multi-framework programs, with SOC 2 packages from around $25,000 per year plus framework fees.
- Secureframe suits price-sensitive small and mid-size teams, with a Fundamentals tier from $7,500 per year and a free trial.
- AuditBoard and ServiceNow GRC are enterprise suites for organizations with dedicated risk teams, at custom, higher pricing.
- The platform license is only one cost line: add the audit fee, penetration test, framework fees and renewal terms before comparing totals.
Quick comparison
| Product | Ideal for | Price from | Free version | |
|---|---|---|---|---|
| Vanta | Integration breadth | See website | No | Visit |
| Drata | Multi-framework monitoring | See website | No | Visit |
| Secureframe | Guided SMB onboarding | See website | Free trial | Visit |
| AuditBoard | Enterprise GRC and audit | See website | No | Visit |
| ServiceNow GRC | ServiceNow ecosystems | See website | No | Visit |
 Sprinto | Budget SOC 2 automation | See website | No | Visit |
 Hyperproof | Flexible multi-framework GRC | See website | No | Visit |
 LogicGate | Custom risk workflows | See website | No | Visit |
The best grc compliance platforms
These eight platforms cover compliance automation for startups and enterprise GRC for large organizations. We compared official pricing pages, marketplace listings and public reviews, focusing on framework coverage, evidence automation and the true annual cost, since most vendors quote after a demo.
Vanta
Ideal for: Integration breadth
Vanta is the most established compliance automation platform in this list, with the broadest integration library for collecting evidence automatically from cloud, identity and HR tools. It covers SOC 2, ISO 27001, HIPAA and other frameworks, monitors controls continuously, and its Trust Center lets you share your security posture with customers without manual questionnaires.
Marketplace listings put Essentials at $14,000 per year for 1 to 20 employees, with typical yearly costs around $20,000 once frameworks and add-ons are included, and the audit itself is billed separately by a CPA firm. For a cloud-native company that needs SOC 2 to close deals, Vanta's breadth and maturity make it a safe first choice.
- Broadest integration library
- Automated evidence collection
- Trust Center for sharing security posture
- Essentials from $14,000 per year in marketplace listings
- Audit billed separately
Drata
Ideal for: Multi-framework monitoring
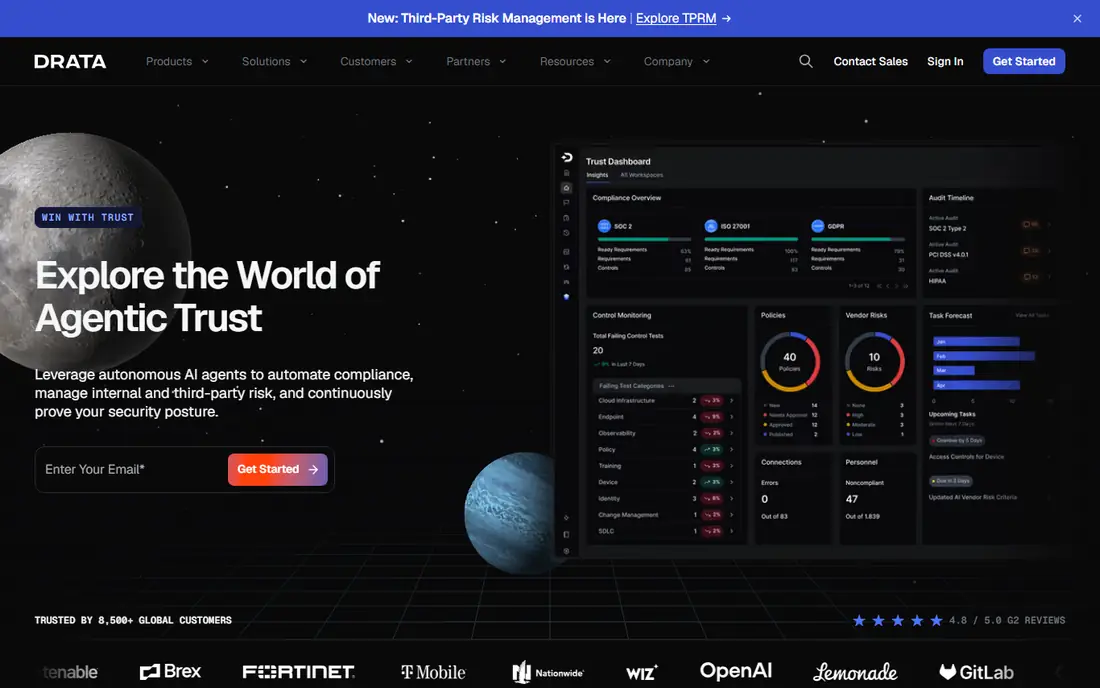
Drata is the strongest pick for multi-framework programs and continuous monitoring. It automates evidence collection, monitors controls in real time, and handles SOC 2, ISO 27001, HIPAA and newer AI governance frameworks, including AI risk classification aligned to ISO 42001. Its monitoring experience is frequently rated as the smoothest among the automation platforms.
Marketplace listings cite around $25,000 per year plus $7,500 per framework for a 100-employee organization, with audits for small to mid-size companies adding $12,000 to $20,000. For a company running several frameworks at once, Drata's monitoring depth justifies the price.
- Strong continuous monitoring
- Multi-framework programs
- AI risk features for ISO 42001
- SOC 2 packages from around $25,000 per year plus $7,500 per framework
- Audit billed separately
Secureframe
Ideal for: Guided SMB onboarding
Secureframe suits small and mid-size teams that want guided onboarding without enterprise complexity. Its platform automates evidence collection, policy management and audit preparation for SOC 2, ISO 27001, HIPAA and other frameworks, with a Fundamentals tier listed at $7,500 per year for one framework. A free trial, unusual in this category, lets teams test before committing.
The audit itself is not included, only audit support, and AI governance coverage is thinner than Drata's or Vanta's in 2026 comparisons. For a price-sensitive team starting its first SOC 2, Secureframe's low entry price and guided setup are appealing.
- Guided onboarding for SMBs
- Fundamentals tier from $7,500 per year
- Free trial available
- AI governance detail is thinner than Drata or Vanta
- Audit support only, not the audit itself
AuditBoard
Ideal for: Enterprise GRC and audit
AuditBoard, now listed in some comparisons under its Optro branding, is the enterprise GRC standard in this list. It covers SOX compliance, internal audit, risk management and controls testing for large, regulated organizations with dedicated risk teams, going well beyond the SOC 2 automation that startups need.
Pricing is custom and typically $50,000-plus per year, which puts it out of reach for small teams. For a large company that needs enterprise-wide control inventory, board reporting and audit workflows, AuditBoard is the right tier. For a first SOC 2, start with Vanta, Drata or Secureframe instead.
- Enterprise GRC standard
- SOX, audit and risk workflows
- Strong for large, regulated companies
- Custom pricing, typically $50,000-plus per year
- Overkill for a first SOC 2
ServiceNow GRC
Ideal for: ServiceNow ecosystems
ServiceNow GRC suits large organizations already running ServiceNow for ITSM and operations. It adds governance, risk and compliance workflows on the same platform, with policy management, risk assessment and audit support that connect to the service data teams already use.
Pricing starts around $50,000 per year in comparisons, and the value depends on ServiceNow adoption. For a ServiceNow enterprise, it consolidates risk work onto one platform. For others, a dedicated compliance tool will be cheaper and faster to deploy.
- Deep ServiceNow integration
- Enterprise risk and compliance workflows
- Strong for large ServiceNow customers
- Pricing from around $50,000 per year
- Best value only inside ServiceNow
Sprinto
Ideal for: Budget SOC 2 automation
Sprinto is a budget-friendly compliance automation option for startups pursuing SOC 2. Marketplace listings cite $7,500 per year plus $2,000 for the first framework for a starter platform up to 100 employees, with typical yearly costs around $15,000 once frameworks are added. Partner auditors can handle the audit itself.
The ecosystem is smaller than Vanta's, and multi-framework depth is thinner than Drata's. For a startup that needs SOC 2 at the lowest credible price, Sprinto is worth a quote alongside Secureframe.
- Lower entry pricing
- SOC 2 focus
- Partner auditors available
- Starter from $7,500 per year plus $2,000 for the first framework
- Smaller ecosystem than Vanta
Hyperproof
Ideal for: Flexible multi-framework GRC
Hyperproof suits teams managing many frameworks that want flexible control mapping, so one control can satisfy several standards without duplicate work. Collaboration tools help distributed compliance teams gather evidence and track issues in one place.
Pricing is not published, with quotes by proposal only, so budget comparisons require a sales conversation. For a mid-market team juggling SOC 2, ISO 27001 and HIPAA together, Hyperproof's mapping flexibility is a genuine advantage.
- Flexible control mapping across frameworks
- Good for teams managing many standards
- Strong collaboration
- No published pricing
- Proposal-based quotes only
LogicGate
Ideal for: Custom risk workflows
LogicGate is the customizable GRC option, with a no-code builder for risk, compliance and audit workflows that teams can shape to their own processes. That flexibility suits organizations whose risk workflows do not fit a standard template, and its reporting helps leadership track control health.
Pricing is custom, and the flexibility requires configuration effort upfront. For a team that wants GRC software to match its processes rather than the other way around, LogicGate is a strong pick.
- No-code workflow builder for risk and compliance
- Customizable for unique processes
- Strong reporting
- Custom pricing
- Needs configuration effort to match your processes
How we picked these
We compared official pricing pages, marketplace listings and public reviews for GRC and compliance platforms available in October 2026. We favored platforms with a real user base, current framework coverage and a clear pricing path, and we weighed evidence automation, monitoring depth, framework breadth and total annual cost, since the license alone understates the real spend.
What to check before you choose a GRC platform
Start with your trigger. If a customer or deal requires a SOC 2 report, buy compliance automation such as Vanta, Drata or Secureframe, which gets you audit-ready fastest. If the board wants an enterprise-wide control inventory, buy a GRC suite such as AuditBoard or ServiceNow GRC. Buying the wrong tier wastes money in either direction.
Then price the full year, not just the license. Add the audit fee from a CPA firm, a penetration test if customers expect one, a fee per framework beyond the first, and the renewal terms, since most vendors price added frameworks separately and renewal increases are common. Ask for a renewal cap and evidence-export rights before signing, since switching mid-audit can restart the observation clock.
Finally, test the integration with your stack. Connect your cloud, identity and HR tools in a trial and check how much evidence is collected automatically versus manually. A platform that automates 80 percent of evidence saves months of work, while one that only produces configuration evidence leaves your team gathering logs by hand.
Frequently asked questions
What is the best GRC compliance platform?
Vanta leads on integration breadth, Drata on multi-framework monitoring, and Secureframe on price for small teams. AuditBoard and ServiceNow GRC suit large enterprises with dedicated risk teams.
How much does compliance automation cost?
Entry-level single-framework deployments typically start around $7,500 to $14,000 per year, multi-framework deployments commonly land between $15,000 and $60,000 annually, and enterprise GRC contracts can exceed $100,000. Audit fees from a CPA firm are billed separately.
Does a compliance platform include the audit?
No, the platform gets you audit-ready, and an independent CPA firm performs the audit and issues the report, billed separately. Some vendors bundle audit support or partner auditors, but the audit itself is a separate cost.
How long does a first SOC 2 take?
A SOC 2 Type 1 can be audit-ready within weeks to a couple of months on a clean cloud stack. A Type 2 also needs an observation window, commonly three to twelve months, while the platform monitors your controls.
What is the difference between GRC software and compliance automation?
Compliance automation focuses on getting a specific certification such as SOC 2 or ISO 27001 by automating evidence and monitoring. GRC software is broader, covering governance, risk management and audit workflows across the enterprise.